Quick answer: An SSL handshake is the short exchange a browser and a server run before any HTTPS page loads. In it they agree on a TLS version and a cipher suite, the server proves its identity with its certificate, and both sides create the same symmetric session keys — without ever sending those keys across the network. The whole thing takes milliseconds: one network round trip with TLS 1.3, two with the older TLS 1.2. After the handshake, everything you send and receive is encrypted.
Every time you open a website that starts with https, your browser and the server have a quick, invisible conversation before a single word of the page is sent. That conversation is the SSL handshake — more accurately called a TLS handshake, because SSL is the old name for the protocol and TLS is what actually runs today. It is the reason the padlock appears in your address bar, and it is the reason nobody sitting between you and the website can read your passwords, your messages, your card number, or the photos you upload.
This guide explains what the handshake is, what it has to achieve, exactly what happens step by step in TLS 1.3 and TLS 1.2, how the two versions differ, why it uses two kinds of encryption, what goes wrong when it fails, and how to watch one happen yourself.
What an SSL handshake actually does
A handshake solves three problems before any page data is sent. First, the two sides agree on the rules: which version of TLS they will speak and which cipher suite — the agreed bundle of algorithms — they will use to encrypt everything afterwards. Second, the server proves who it is: it presents its certificate, and the browser checks that a trusted certificate authority issued it, that it has not expired, and that it matches the hostname in the address bar. Third, both sides create the same shared secret keys, which they will use for fast symmetric encryption for the rest of the session.
A useful way to picture it is two strangers meeting to exchange a secret. First they agree on a language and a code (the version and cipher suite). Then one of them shows an ID card issued by an authority they both trust (the certificate). Then they work out a shared secret code word together, in a way that anyone listening in cannot work it out (the key exchange). After that, they talk in code — quickly, because a shared code is much faster than the slow public-key maths they used to set it up.
One point worth clearing up early: the handshake is not the encrypted session itself. It is the short negotiation that sets the session up. The padlock in your browser means the handshake succeeded and the session is encrypted — it does not mean the website itself is honest. A scam site can have a perfectly valid certificate and a perfect handshake. The handshake proves you are talking to the real owner of that domain name, not that the owner is trustworthy.
The TLS 1.3 handshake, step by step
TLS 1.3 is what most browsers and servers negotiate today, and it is the fastest version of the handshake ever standardised. The whole exchange takes a single network round trip. Here is what happens, in order.
1. ClientHello. Your browser opens the connection and sends the first message. It lists the TLS versions and cipher suites it supports, a random number, the hostname it wants — Server Name Indication, or SNI, which tells a server hosting many sites which certificate to present — and the application protocols it speaks, through ALPN (usually HTTP/2 or HTTP/1.1). Crucially, it also sends a key share: its half of a Diffie-Hellman key exchange, made with a guess at the key-exchange group the server will accept. Sending the key share up front is the trick that makes TLS 1.3 a one-round-trip handshake.
2. ServerHello. The server picks the TLS version and cipher suite, and replies with its own key share. At this point both sides can compute the same shared secret, and every message after this one is encrypted. That is a major change from TLS 1.2, where the server’s certificate travelled across the network in the clear.
3. EncryptedExtensions. The server answers the client’s remaining requests — for example, which application protocol was chosen through ALPN — under encryption.
4. Certificate and CertificateVerify. The server sends its certificate chain, and then a signature over the entire handshake so far, made with the certificate’s private key. That signature is the proof of identity: a copied certificate is useless without the matching private key, and the browser verifies the chain against its list of trusted certificate authorities.
5. Finished, from both sides. Each side sends a Finished message — a cryptographic checksum over the whole handshake — which proves nobody tampered with any of the messages in transit. Then application data flows: the browser’s request for the page, and the server’s response, all encrypted with the session keys.
If the client guessed a key-exchange group the server does not support, the server sends a HelloRetryRequest and the client tries again with a different group, which costs one extra round trip. Modern browsers are also beginning to offer post-quantum hybrid key shares — OpenSSL 3.5, for example, offers X25519MLKEM768 alongside the classic X25519 — so the key exchange stays safe even if large quantum computers arrive.
| Message | Who sends it | What it does |
|---|---|---|
| ClientHello | Browser | Versions, cipher suites, random value, SNI hostname, ALPN, key share |
| ServerHello | Server | Chosen version and cipher, own key share |
| EncryptedExtensions | Server | Answers to the client’s other requests (e.g. ALPN choice) |
| Certificate | Server | Certificate chain proving the server’s identity |
| CertificateVerify | Server | Signature proving the server holds the private key |
| Finished | Both sides | Checksum proving nothing was tampered with |
The TLS 1.2 handshake
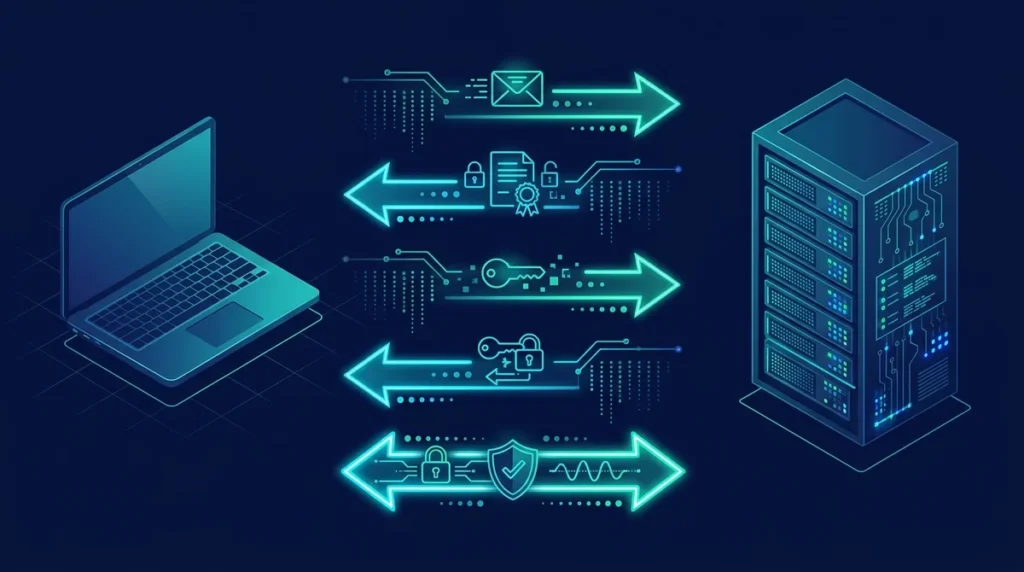
TLS 1.2 is still widely supported and is the fallback for older clients, but it needs two round trips instead of one, and it does several things in the open that TLS 1.3 encrypts.
1. ClientHello. The browser sends the TLS versions and cipher suites it supports, a random number, and the hostname (SNI). Unlike TLS 1.3, it sends no key share — the key exchange has not started yet.
2. ServerHello, Certificate, ServerHelloDone. The server picks the version and cipher suite, sends its certificate in the clear, and signals that it is done with its half of the negotiation.
3. ClientKeyExchange. The browser creates a pre-master secret, encrypts it with the server’s public key from the certificate, and sends it to the server. Only the server can decrypt it, because only the server holds the matching private key. Both sides then derive the same master secret and session keys from it.
4. ChangeCipherSpec and Finished, from both sides. Each side announces that everything from now on will be encrypted, and sends a Finished message proving the handshake was not tampered with. Then application data flows.
The important weakness in this design is the RSA key transport in step 3: the pre-master secret is encrypted with the server’s long-term public key. If someone records the traffic and later steals the server’s private key, they can decrypt the session. TLS 1.3 removed RSA key transport entirely, which is why it can promise forward secrecy for every connection.
TLS 1.2 vs TLS 1.3
| Feature | TLS 1.2 (2008) | TLS 1.3 (2018) |
|---|---|---|
| Full handshake round trips | 2 | 1 (0 on resumption) |
| Cipher suites | 30+ (including RC4, 3DES, CBC) | 5, all AEAD |
| Key exchange | RSA, DH, ECDH, DHE, ECDHE | ECDHE only |
| Forward secrecy | Optional | Mandatory |
| Server certificate | Sent in the clear | Encrypted after ServerHello |
| RSA key transport | Supported | Removed |
| CBC-mode ciphers | Supported | Removed |
| Session resumption | Session IDs / tickets | Pre-shared keys, 0-RTT |
| Handshake encryption | Mostly cleartext | Encrypted after ServerHello |
The practical difference for a normal user is speed and safety. A TLS 1.3 handshake is one round trip instead of two, so the page starts loading sooner — and because the certificate and the rest of the handshake are encrypted, an observer on the network learns far less about the connection. The extra round trip matters most on slow or distant connections, where each round trip can cost a tenth of a second or more.
The guide to reducing ping covers what round trips cost in practice and the fixes that matter most when a connection feels slow.
Why the handshake uses two kinds of encryption
The handshake leans on asymmetric cryptography — a public key and a private key — because it solves the problem of agreeing on a secret with a stranger over an open network. The server’s public key is in its certificate for anyone to see; its private key never leaves the server. The browser can encrypt something only the server can read, and the server can sign something only it could have signed. But asymmetric maths is slow — far too slow to encrypt a whole web page.
So the handshake uses asymmetric cryptography only briefly, to agree on a shared secret, and then both sides switch to symmetric encryption — one shared key, used by both sides — for the actual data. Symmetric ciphers like AES-GCM and ChaCha20-Poly1305 are fast enough to encrypt gigabytes without anyone noticing. That switch is the whole point of the handshake: slow, secure maths to set up fast, secure maths.
Forward secrecy is the property that makes this design safe even if something goes wrong later. In TLS 1.3, the key exchange uses ephemeral Diffie-Hellman: fresh keys are generated for every single connection and thrown away when it ends. Even if someone records your traffic today and steals the server’s private key next year, they cannot decrypt what they recorded, because the session keys were never derived from the long-term key. TLS 1.2 only had forward secrecy when the server chose an ephemeral cipher suite; TLS 1.3 makes it mandatory.
Session resumption: skipping the full handshake
A full handshake is fast, but browsers and servers still skip it when they can. If you have visited a site before, the two sides can resume the session instead of doing the whole exchange again.
In TLS 1.2, resumption used session IDs or session tickets: the server hands the client a ticket on the first visit, and the client presents it on the next one to pick up where they left off. In TLS 1.3, resumption uses pre-shared keys, and it can go further: 0-RTT resumption lets the client send its first application data — the request for the page — in the very first message, with no round trip at all.
0-RTT has one catch, and it is worth knowing. Data sent in the first flight can be replayed by an attacker: the request could be delivered twice. That is harmless for a request that only reads a page, but dangerous for one that changes something — placing an order, sending money, changing a password. So servers should only accept idempotent requests, like simple page loads, in 0-RTT, and browsers and servers are careful about when they use it.
How often a handshake happens at all depends on how you connect. On a home connection it happens once per site visit, and the cost is invisible. On a mobile connection the cost is more noticeable, because every round trip crosses the radio network.
The guide to how mobile data works explains the path from your phone to the tower and beyond, and why a distant server costs more round trips than a near one.
Mutual TLS: when the client proves itself too
In a normal handshake, only the server proves who it is. The browser never shows a certificate, and the server never asks for one. But the handshake has an optional step for the other direction: mutual TLS, or mTLS, where the server asks the client for a certificate too, and the client must prove it holds the matching private key.
You will almost never meet mTLS as an ordinary web user. It is used where a service needs to be sure exactly which machine or service is calling it: internal company APIs, a bank’s connection to a payment processor, or a device phoning home to its manufacturer. If you have ever seen a website ask you to pick a certificate from a list, that was mTLS. For everything else, the server’s certificate plus your login — ideally with two-factor authentication — is the proof that matters.
What can go wrong: handshake failures
A failed handshake usually shows up as a browser error page instead of the website. The message tells you roughly what went wrong, and the fix depends on which one it is.
| Browser error | What it usually means | What to do |
|---|---|---|
| ERR_SSL_PROTOCOL_ERROR / SSL_ERROR_RX_RECORD_TOO_LONG | Browser and server could not agree on a TLS version or cipher suite | Update the browser; if the site is old, it may only support retired TLS versions |
| NET::ERR_CERT_DATE_INVALID / certificate expired | The site’s certificate has expired | Nothing to fix on your side — the site owner must renew; do not click through |
| NET::ERR_CERT_COMMON_NAME_INVALID | Certificate does not match the hostname | Usually the site’s problem (wrong certificate installed); check you typed the address correctly |
| NET::ERR_CERT_AUTHORITY_INVALID / self-signed | Certificate was not issued by a trusted authority | Do not proceed on a site asking for passwords or payment; on a local device (router, printer) it is often expected |
| ERR_SSL_VERSION_OR_CIPHER_MISMATCH | No shared TLS version or cipher | Update the browser and the operating system; very old devices cannot do TLS 1.2+, and if your phone is one of them, it is time to look at a current Android phone |
| Your connection is not private (generic) | Certificate problem of some kind | Check the date and time on your device first — a wrong clock breaks certificate checks |
The date-and-time check is the one most people miss. Certificates are only valid between two dates, and your device checks them against its own clock. If the clock is months off, every certificate looks expired or not-yet-valid, and every HTTPS site fails at once. The same failure on every site points at your device; a failure on one site points at that site.
A related point: a certificate problem and a DNS problem can look alike in the browser, because both stop the page loading before anything renders. If the address itself does not resolve, the handshake never even starts.
The guide to fixing a DNS server that is not responding covers the DNS side, including when the problem is your network and when it is the site.
And if your phone shows SOS, there is no connection at all — no handshake can even begin, because the phone is not on any network.
The guide to what SOS means on iPhone explains why it appears and how to fix it.
On public Wi-Fi, the handshake is what keeps you safe: the network owner can see that you connected to a site, but the handshake’s encryption means they cannot read what you send. That is true on a mobile hotspot too, where the connection is yours rather than the café’s.
The guide to whether a hotspot uses data covers what a hotspot actually costs you, and the handshake on it works exactly the same as on any other connection.
One fix you will see recommended for stubborn handshake errors is resetting the device’s network settings. It works because it clears corrupted certificates, proxies and DNS settings in one go — but it also forgets every saved Wi-Fi network and Bluetooth pairing, so it is worth backing up first.
The guide to backing up an Android phone covers the full process, and it takes ten minutes.
How to see a handshake yourself
You do not have to take any of this on trust. Two tools let you watch a handshake happen.
In the browser. Open any HTTPS site, click the padlock (or the tune icon) in the address bar, then “Connection is secure” and “Certificate is valid” to see the certificate: who issued it, which hostname it covers, and when it expires. In Chrome’s DevTools, the Security tab shows the TLS version, the cipher suite, and whether the certificate is valid — the same facts the handshake negotiated, shown plainly. The same steps work on a Chromebook, since it runs Chrome — the guide to Chromebook vs laptop covers which machine fits which kind of user.
From the command line. OpenSSL’s s_client tool prints every handshake message:
openssl s_client -connect example.com:443 -servername example.com -tls1_3The output shows the certificate chain, the negotiated TLS version and cipher, and the session details. Add -msg to see each handshake message as it is sent and received. If the handshake fails, s_client names the exact problem — a much better error than the browser’s generic page.
How long does a handshake take — and does it slow the web?
A TLS 1.3 handshake is one round trip: the time for a message to reach the server and the reply to come back. On a nearby server that is a few milliseconds; on a server on another continent it can be 100 milliseconds or more. TLS 1.2 doubles that, because it needs two round trips. That is why the move to TLS 1.3 mattered for speed, and why session resumption and 0-RTT exist: most of the cost of the handshake is the waiting, not the maths.
Content delivery networks cut the cost further by ending the TLS connection close to you. When you open a popular site, the handshake usually happens with an edge server in your own country, not with the site’s origin server thousands of kilometres away.
The guide to what a content delivery network is explains how that edge works, and why it makes both the handshake and the page faster.
There is one more change coming that makes the handshake matter more, not less. Public TLS certificates are getting shorter-lived: the maximum lifetime fell to 200 days on 15 March 2026, and the industry schedule heads toward 47 days by 2029. Shorter certificates mean less damage if one is stolen, but they also mean site owners must automate renewal — a certificate that used to be renewed once a year will soon need renewing every few weeks. If you run a website, that is the handshake-related job to automate now.
Frequently asked questions
What is an SSL handshake in simple words?
It is the short conversation a browser and a server have before any page data is sent: they agree on encryption rules, the server proves its identity with its certificate, and both sides create the same session keys. After that, everything is encrypted. It takes milliseconds.
Is an SSL handshake the same as a TLS handshake?
Yes, in practice. SSL is the old name; the protocol running today is TLS, and the handshake is a TLS handshake. People still say “SSL handshake” because the term stuck, and this guide uses both names the same way.
How many steps are in an SSL handshake?
In TLS 1.3: ClientHello, ServerHello, EncryptedExtensions, Certificate, CertificateVerify, and Finished from both sides — one network round trip. In TLS 1.2 the same job takes two round trips, with a separate ClientKeyExchange step.
What is the difference between TLS 1.2 and TLS 1.3 handshakes?
TLS 1.3 needs one round trip instead of two, encrypts the handshake after ServerHello, uses only five modern cipher suites, makes forward secrecy mandatory, and removes RSA key transport and CBC ciphers. TLS 1.2 is still secure when configured properly, but it is slower and shows more of the handshake in the clear.
Why does the handshake use both public-key and symmetric encryption?
Public-key cryptography solves the problem of agreeing on a secret with a stranger, but it is too slow to encrypt a whole page. So the handshake uses it briefly to agree on a shared secret, then switches to fast symmetric encryption for the data. That is why the handshake exists at all.
What happens if the SSL handshake fails?
The browser shows an error page instead of the site — for example, a certificate-expired or cipher-mismatch error. The cause is usually an expired or mismatched certificate on the site, an outdated browser or operating system, or a wrong date and time on your device.
Does an SSL handshake happen on every page load?
A full handshake happens on the first visit to a site. On repeat visits the browser and server usually resume the session instead, skipping most of the exchange — and TLS 1.3 can even send the first request with zero round trips (0-RTT).
Is the padlock enough to trust a website?
No. The padlock means the handshake succeeded and the connection is encrypted — it proves you are talking to the real owner of that domain name. It says nothing about whether that owner is honest. A scam site can have a valid certificate and a perfect handshake.
Bottom line
An SSL handshake is the brief negotiation that makes HTTPS possible: agree on the rules, prove the server is who it claims to be, and create shared keys that encrypt everything afterwards. TLS 1.3 does it in a single round trip, with forward secrecy and an encrypted handshake; TLS 1.2 takes two trips and shows more in the clear. When it fails, the browser’s error message usually tells you whether the problem is the site’s certificate, your outdated software, or your own device’s clock. And the padlock it produces is a promise about encryption, not about trust — the handshake proves who you are talking to, not whether they deserve it.
Continue Reading on CripsyWire
For more practical tutorials and hidden features, see our full how-to guides section. AI workflow guides feed into the broader AI tools and agents coverage, phone tricks live in smartphones, and wearable setup walkthroughs in wearables. When you are deciding what to buy, the reviews and comparisons section helps. All part of CripsyWire Tech, and the homepage shows what is newest.